


As the Fortinet industry enters an era of unprecedented change, our company is strong, lucid, focused, and eager to exceed our customers’ expectations. We will continue to pursue our passion for better performance and human-centric technology of NSE4_FGT_AD-7.6 pass-sure questions. With our heads and our hearts, we are dedicated to creating distinctive NSE4_FGT_AD-7.6 exam and customer-friendly innovations. That's the first element of our mission for the future. The second, equally important element is to earn the long-term trust of our customers through quality and care in everything we do (NSE4_FGT_AD-7.6 guide torrent).
NSE4_FGT_AD-7.6 exam is a powerful proof of the working ability of every Fortinet worker. It's necessary for you to pass exam and get an exam certification which makes you ahead of your fellow workers. With NSE4_FGT_AD-7.6 exam torrent, you will be much more competitive and get more promotion opportunities. We strive for providing you a comfortable study platform (NSE4_FGT_AD-7.6 pass-sure questions) and continuously upgrade exam to meet every customer's requirements.
Here are several advantages about our NSE4_FGT_AD-7.6 guide torrent files for your reference. We sincere hope you spare some time to have a glance over our website and the following items.

Free download demo before payment
Our webpage provide you three kinds of NSE4_FGT_AD-7.6 guide torrent demos to download for free. Before you decide to buy, you can have a careful knowledge of the exam by downloading any demo version you want. PDF version of NSE4_FGT_AD-7.6 exam torrent has excellent format, you can print exam questions out or just download in your digital appliance. You can experience the simulated actual test on PC test engine, which is a better way for you to adapt to the NSE4_FGT_AD-7.6 pass-sure questions in advance. You can also choose the online test engine of NSE4_FGT_AD-7.6 guide torrent, which means you can use in any electronic devices at any time after you have opened the NSE4_FGT_AD-7.6 exam torrent once in an online environment.
One-year free update
In accordance with the actual exam, we provide the latest NSE4_FGT_AD-7.6 exam torrent for your practices. After you pay for our product, we will send you the updated NSE4_FGT_AD-7.6 guide torrent within 5-10 minutes. What's more, you have no need to spend extra money updating your NSE4_FGT_AD-7.6 pass-sure questions our company will ensure your one-year free updates. You just need to check your mailbox and take your time to study.
Fortinet NSE4_FGT_AD-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
Reference: https://training.fortinet.com/local/staticpage/view.php?page=fortios_administrator_exam
Pay more attention to privacy protection
Nowadays, data breaches happen every day in both the public and private sectors. Our company focuses on protecting every customer's personal information while they are using the NSE4_FGT_AD-7.6 guide torrent. And we have built a complete set of security measures about NSE4_FGT_AD-7.6 pass-sure questions, any illegal behavior will be punished severely. Therefore, you can use in a safe environment.
Instant Download NSE4_FGT_AD-7.6 Exam Braindumps: Upon successful payment, Our systems will automatically send the product you have purchased to your mailbox by email. (If not received within 12 hours, please contact us. Note: don't forget to check your spam.)
100% guaranteed pass rate
With 10 years’ development, we promise to help you pass exam. Supported by our professional expert team, our NSE4_FGT_AD-7.6 exam torrent has grown up and has made huge progress. We have confidence to deal with your difficulties directing at your own situation while you are using the NSE4_FGT_AD-7.6 pass-sure questions. It's our responsibility to guarantee you pass exam for your trust in our NSE4_FGT_AD-7.6 exam torrent. We are committed to invest all efforts to making every customers get Fortinet examination certification.
Fortinet NSE 4 - FortiOS 7.6 Administrator Sample Questions:
An administrator wants to form an HA cluster using the FGCP protocol. Both FortiGate devices are configured with the set override enable command. Arrange the criteria in the order in which the FGCP protocol uses them to elect the primary FortiGate. Select the criteria in the left column, hold and drag it to a blank position in the column on the right. Place the four correct steps in order, placing the first step in the first position. Once you place a step, you can move it again if you want to change your answer before moving to the next question. You need to drop four criteria in the work area. Select and drag the screen divider to change the viewable area of the source and work areas. (Choose four answers)
Correct Answer:
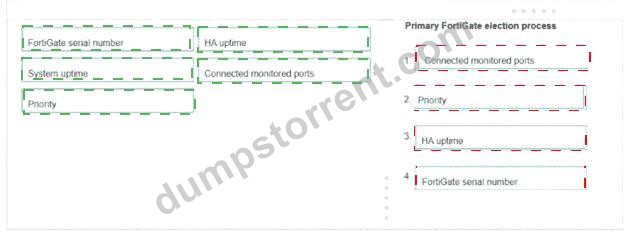
Explanation:
"This slide shows the different criteria that a cluster considers during the primary FortiGate election process.
The criteria order evaluation depends on the HA override setting."
For the default case shown in the guide:
"1. The cluster compares the number of monitored interfaces that have a status of up. The member with the most available monitored interfaces becomes the primary.
2. The cluster compares the HA uptime of each member...
3. The member with the highest priority becomes the primary.
4. The member with the highest serial number becomes the primary."
For this question's case:
"If the HA override setting is enabled, the priority is considered before the HA uptime ." Technical Deep Dive:
Because override is enabled , the election order changes from the default sequence. The first criterion is still Connected monitored ports , because interface health is evaluated first. After that, Priority moves ahead of HA uptime . If those still do not decide the winner, FortiGate uses the serial number as the final tie-breaker.
Therefore the correct order is:
1. Connected monitored ports
2. Priority
3. HA uptime
4. FortiGate serial number
This distinction matters in production. With set override enable, you are effectively making HA priority authoritative over uptime, so the preferred unit will reclaim the primary role when it comes back online. That is useful for deterministic primary selection, but it can also cause an additional failover event when the preferred chassis returns to service. The guide explicitly notes this tradeoff.
In practice, the relevant HA checks and verification commands are:
show system ha
get system ha status
diagnose sys ha status
These let you confirm override status, device priority, monitored interfaces, and recent election results. From a control-plane perspective, FGCP election logic is handled by FortiOS over heartbeat links, while data-plane forwarding after election continues using the cluster's virtual MAC behavior and synchronized HA state.
Refer to the exhibits.


A diagram of a FortiGate device connected to the network VIP object and firewall policy configurations are shown.
The WAN (port2) interface has the IP address
100.65.0.101/24.
The LAN (port4) interface has the IP address
10.0.11.254/24.
If the host 100.65.1.111 sends a TCP SYN packet on port 443 to 100.65.0.200. what will the source address, destination address, and destination port of the packet be at the time FortiGate forwards the packet to the destination?
- A. 100.65.1.111, 10.0.11.50. and 443. respectively
- B. 10.0.11.254, 100.65.0.200. and 443, respectively
- C. 10.0.11.254, 10.0.15.50, and 4443. respectively
- D. 100.65.1. 111, 10.0.11.50, and 4443. respectively
Correct Answer: D 🗳️
Explanation: Only visible for DumpsTorrent members. You can sign-up / login (it's free).
An administrator manages a FortiGate model that supports NTurbo
How does NTurbo acceleration enhance antivirus performance?
- A. For flow-based inspection. NTurbo establishes a dedicated data path to redirect traffic between the IPS engine and FortiGate ingress and egress interfaces.
- B. For proxy-based inspection. NTurbo buffers the whole file and then sends it to the antivirus engine.
- C. For flow-based inspection. NTurbo creates two inspection sessions on the FortiGate device.
- D. For proxy-based inspection. NTurbo offloads traffic to the content processor.
Correct Answer: A 🗳️
Explanation: Only visible for DumpsTorrent members. You can sign-up / login (it's free).
An administrator has configured the following settings.
config system settings
set ses-denied-traffic enable
end
config system global
set block-session-timer 30
end
What are the two results of this configuration? (Choose two.)
- A. The number of logs generated by denied traffic is reduced.
- B. A session for denied traffic is created.
- C. Denied users are blocked for 30 minutes.
- D. Session helpers are disabled for denied traffic.
Correct Answer: A,B 🗳️
Explanation: Only visible for DumpsTorrent members. You can sign-up / login (it's free).
Refer to the exhibit.
A partial cloud topology is shown.
You deployed a FortiGate Cloud-Native Firewall (CNF) in AWS for FortiGate CNF policy enforcement for EC2 instance traffic. Which path does the EC2 traffic take from the EC2 instance to the internet?
- A. EC2 instance # GWLB endpoint (GWLBe) # FortiGate CNF # IGW # internet
- B. EC2 instance # Internet Gateway (IGW) # Gateway Load Balancer (GWLB) # FortiGate CNF # internet
- C. EC2 instance # GWLBe # FortiGate CNF # GWLBe # IGW # internet
- D. EC2 instance # FortiGate CNF # GWLB # GWLBe # IGW # internet
Correct Answer: C 🗳️
Explanation: Only visible for DumpsTorrent members. You can sign-up / login (it's free).
Viewing page 1 out of 20 pages.
Viewing questions 1-5 out of 96 questions.

 Dennis

 Jason

 Carr
 Gary
 Lewis

 Brook
 Jenny
 Leona
 Lou
 Adrian
 Olga
 Riva
 Iris
 Dennis
 Matthew
 Gerald
 Regina
 Bernie


